Pentester's Toolkit 2026: The Best Free Open Source Security Tools
A complete roundup of the best free, open source penetration testing tools for 2026, from operating systems and web scanners to advanced code analysis.
Cybersecurity
Poland published the mObywatel app's source code, but login walls, right-click blocks and missing backend code turned openness into a facade.
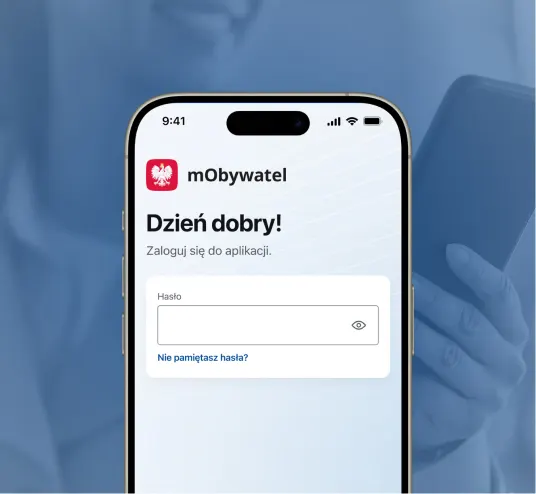
Imagine you're buying a car. The manufacturer promises full transparency and invites you to look under the hood. You open it up and find… a photo of an engine printed on a sheet of cardboard. That is roughly how Poland's IT community felt after the events of December 29, 2025.
After years of announcements and legislative wrangling, the Ministry of Digital Affairs finally did it: it published the source code of the mObywatel app. This is the flagship product of Poland's digital government, used by 11 million Poles. In theory, we should be popping champagne. In practice, we're opening debuggers and rubbing our eyes in disbelief.
What happened in the last days of the year is a fascinating case study of modern public expectations colliding with the military doctrine of "security through obscurity." Let's look at what we actually saw in the mObywatel code, and what we didn't.
The first thing that stands out is how the code was published. In software engineering, the standard is a repository (on GitHub, for example) that shows the change history, the authors and the project structure. What did the Polish government do? It posted static HTML files on the Public Information Bulletin (BIP) website.
It's a textbook case of "malicious compliance." Officials met the legal requirement ("the code has been published"), but did it in a way that makes the code as hard as possible to analyze.
The icing on the cake was protection straight out of the 1990s: right-click and text selection were disabled. mObywatel is supposed to show how modern the Polish state is, so using scripts that any junior developer can bypass in 30 seconds is ironic at best. The community responded almost immediately. Tools that "clean" the code of the government's "protections" appeared online, and repositories with telling names (such as mobywatel-shitcode) took on a life of their own.
This may be the most troubling and counterintuitive part of the story. Just to view the published mObywatel code, you have to sign in with the Trusted Profile (Profil Zaufany), Poland's government e-ID.
The state is building a registry of people interested in analyzing government code. In the eyes of the security services (CSIRT MON), anyone who analyzes the code is a potential threat.
This is the exact opposite of what open source stands for. Open-source security depends on a crowd of anonymous experts (white hats) who hunt for vulnerabilities so they can be fixed. By requiring people to sign in with their full name (and their PESEL national ID number), the state creates a chilling effect. An honest researcher will think twice before landing on a list of "overly curious citizens." A criminal? They'll use a stolen account and review the code without any trouble.
Once you get past the login and the blocks, it turns out the emperor has no clothes. The published code is 75% Kotlin (Android) and 24% Swift (iOS), but it covers mostly the presentation layer. We can see colors, icons and button layouts.
What's missing? Everything that matters. There is no business logic, no server communication code and no backend. We have no way to verify whether the mObywatel app is quietly sending our location data or activity history out through a back door.
Experts compare it to showing off the paint on a building's facade when citizens wanted to check how solid the foundations are. Without visibility into how the app processes data and how it talks to government databases, a security audit is a fiction. What we got is "facade transparency."
The legal status of the mObywatel code could fill a doctoral thesis on absurdity. On one hand, the code was released under the MIT License, one of the most permissive licenses in the world, which allows copying, modification and redistribution. On the other hand, the government added technical copy blocks and limited access to Polish citizens only.
The moment the first user uploaded the code to GitHub (lawfully, and in line with the MIT License), every safeguard put in place by CSIRT MON became pointless. Trying to lock open code inside a cage of national regulations shows how little decision-makers understand the nature of the digital world.
For contrast, look east. Ukraine's Diia app, often held up as a model for mObywatel, has its code on GitHub. It is open to the world, and the government in Kyiv encourages people to submit fixes. Ukraine understood that trust is built through collaboration, not by building digital fortresses.
The December release is sad proof that a doctrine of fear still prevails in Polish public administration. Instead of tapping thousands of Polish developers for a free audit that could make the national app more secure, the government treated them as potential enemies.
mObywatel has effectively become our identity document. In 2026, can we trust a state that demands "digital exhibitionism" from us while hiding behind a screen of bureaucracy and technical incompetence?
Aleksander
Sources:
GitHub repository with the code made public by one of the users
Official announcement from the Ministry of Digital Affairs
Our analysis suggests it is a case of "malicious compliance." Officials met the legal requirement to publish the code, but instead of using a git repository, the industry standard, they chose a format (static HTML files on the Public Information Bulletin, BIP) that makes analysis and automated processing as difficult as possible.
No. What was released is mainly the presentation layer (frontend), written in Kotlin and Swift. The code lacks the core business logic, the backend and the server communication mechanisms, so it's impossible to fully verify how securely citizens' data is processed.
The authorities require a login to identify the people downloading the code. According to the IT community and cybersecurity experts, this creates a "registry of interested parties" and has a chilling effect on independent researchers (white hats), who may skip an audit rather than risk ending up on a list of "suspects."
In theory, yes, because the code was released under the MIT License, which is very permissive. However, the technical blocks on the website (such as disabled text selection) and access limited to Polish citizens contradict both the spirit and the letter of that open license.
The code is available in a GitHub repository, and it can also be downloaded from the official repository after signing in.
Read more
A complete roundup of the best free, open source penetration testing tools for 2026, from operating systems and web scanners to advanced code analysis.
Poland's cyber defense has two faces: the new cyber.gov.pl portal with free tools for citizens, and openly acknowledged offensive cyberweapons.
Poland launches Operation Horizon: 10,000 troops will guard critical infrastructure, and a new MoD app will let citizens report suspicious activity.
A free consultation with one of our experts — no obligation, in full confidence.
Let's talkWe'd like to use Google Analytics cookies to see how many people visit the site and which content is useful. We'll only set them if you agree. You can change your decision at any time via the “Cookie settings” link in the footer. Cookies Policy